What is Bluehorn and how does it protect your organisation?
Bluehorn is Europe's sovereign Extended Detection and Response (XDR) solution. It brings your existing cybersecurity tools together in one intelligent platform, collecting and correlating security data across your IT environment to identify threats, uncover blind spots and support faster response.
Built on proven technology and powered by elite threat operations, Bluehorn combines advanced threat detection, risk scoring and seamless integration with your existing security tools. All within a European approach to cybersecurity, giving your organisation greater visibility and control.
See Bluehorn in action:
Bluehorn in a nutshell
Identify
Know your environment: Bluehorn maps assets and identities across your IT environment, providing visibility into your attack surface and helping uncover vulnerabilities and potential security risks.
Detect
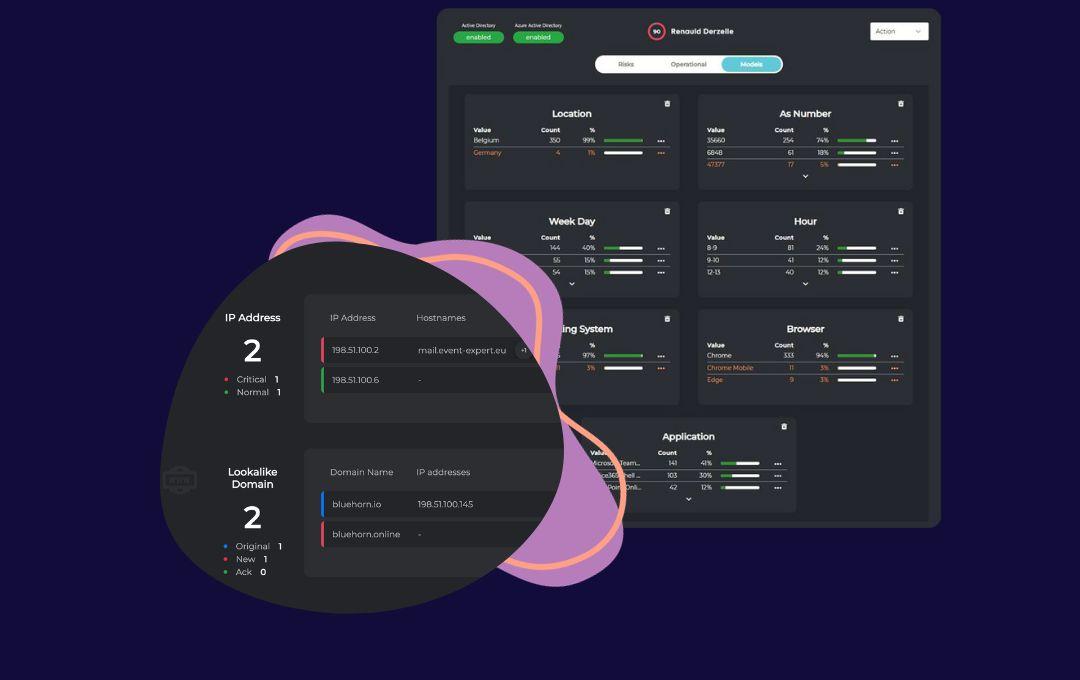
Uncover hidden threats: Bluehorn analyses and correlates security data, logs and network activity to identify abnormal behaviour. By linking threats to specific users and devices, it provides actionable insights through one central console.
Respond
Turn insights into action: With centralised visibility, intelligent risk scoring and streamlined response capabilities, Bluehorn helps your security team prioritise threats and take action faster.
Bridging the gap in today's market that sets many companies up for an unfair battle.
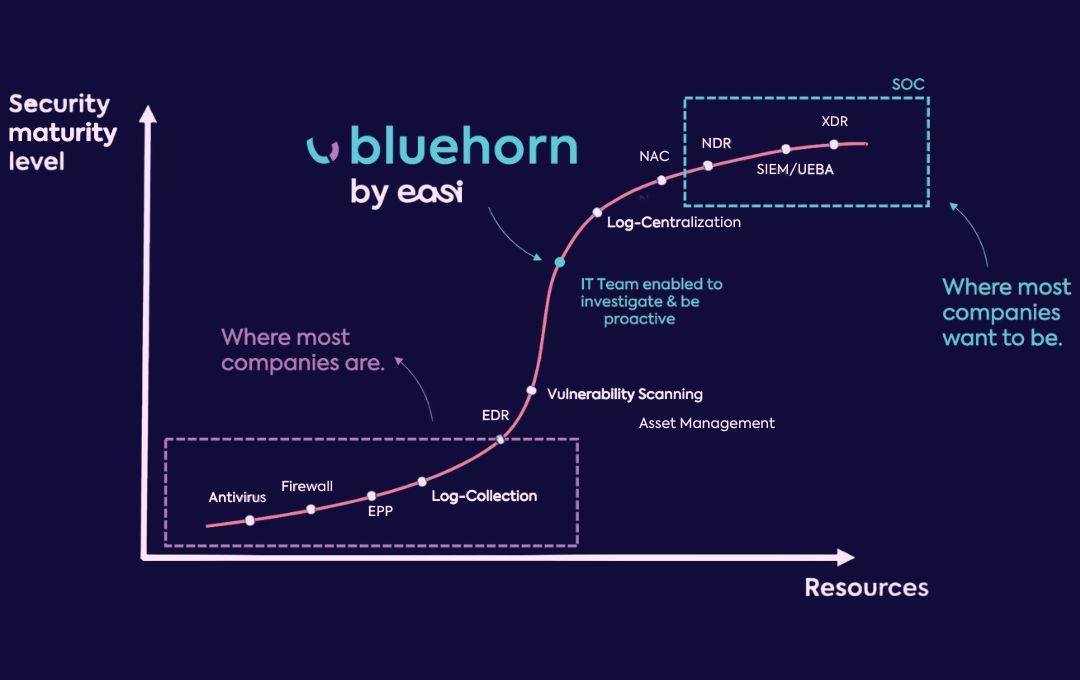
We're here to close that gap
Building a mature cybersecurity environment takes more than deploying individual security tools. Organisations need visibility across their IT environment, the ability to connect security signals and the expertise to investigate and respond to threats.
Yet bringing all these elements together can be complex. Disconnected tools, limited visibility and a lack of specialised expertise can leave organisations exposed.
Technology alone isn't enough
Bluehorn bridges this gap by combining proven security technologies with elite threat operations. It brings your security ecosystem together, helping identify relevant threats, reduce unnecessary alerts and strengthen your organisation's cybersecurity maturity.
Backed by Easi's own SOC, Bluehorn goes beyond collecting security data. It turns information into actionable intelligence, helping security teams focus on the threats that matter.
Reduce your attack surface. Shorten threat dwell time from months or weeks to days.
Bluehorn is a European Extended Detection and Response (XDR) solution developed by Easi. It collects and correlates security data from across an organisation's IT environment to identify suspicious activity, assess risks and support threat response. The platform is built on established security technologies and powered by elite threat operations.
How does Bluehorn's XDR platform work?
Bluehorn acts as a unified XDR-platform (Extended Detection and Response), collecting and correlating data from multiple sources across your IT environment, including your existing security tools.
Built on proven technology and powered by elite threat operations, it turns this data into actionable insights, helping you identify threats faster, assess risks and respond more effectively.
In addition to that
Risk scoring
Bluehorn assesses the risk associated with assets and identities, helping you understand which ones may be compromised and where action is needed.
Seamless integration
Bluehorn integrates with your existing security ecosystem, building on the investments you've already made in cybersecurity.
Built-In Intelligence
Bluehorn analyses raw data, including logs and network traffic, to identify suspicious behaviour and turn it into actionable alerts.
Detection and Response
Bluehorn detects and responds to security threats that get past your prevention tools, such as firewalls and antivirus solutions, helping you act quickly when it matters. A unique characteristic.
"We conducted a POC of the BlueHorn solution along with SOC support from Easi. They convinced us to test it based on our longstanding relationship and mutual trust. Quickly, the tool and services demonstrated their strength and justified their value by providing significant visibility and recommendations.
Overall, implementing this SOC solution has been an excellent decision for our company. We feel more secure and confident in our ability to manage potential threats, allowing us to focus on our daily operations with greater peace of mind. I would recommend this solution to any organisation looking to strengthen its cybersecurity."
Xavier Moumal – Head of IT Benelux, Monnoyeur
What are Bluehorn's main capabilities?
-
Asset discovery
Keep track of active and inactive resources across your IT environment, including cloud, virtual and physical devices.
Bluehorn gives you greater visibility into your assets and helps uncover potential security risks.
-
Advanced analysis
Bluehorn uses its own security analysis modules to process data from sources such as DNS, network traffic, Microsoft 365 and Cyber Threat Intelligence (CTI).
This allows it to deliver valuable insights, even without direct integration with your firewall or antivirus software.
-
Risk Exposure Monitoring
Bluehorn maps your risk exposure and monitors the dark web for leaked credentials, helping you identify vulnerabilities and blind spots before attackers can exploit them.
-
Open solution
Bluehorn integrates with your existing security ecosystem through dedicated connectors, bringing data from different security solutions together.
Its intelligent correlation helps eliminate duplicate alerts and gives you a clearer overview of potential threats.


Daily management
Get a clear overview of your security environment. Identify risks and prioritise what matters.
Plug & play
Seamlessly connect Bluehorn to your existing security ecosystem . Bring everything together in one platform for optimal data-driven decisions.
Maintain focus
Reduce security noise and focus on relevant threats. Free up time for strategic priorities.
Work more agile
Manage security yourself or rely on your security partner. Get expert support when you need it.
An all-round solution
No need to compromise between different solutions. Bluehorn offers the same functionalities as other efficient security solutions, such as a XDR or a SIEM.
Big Brother effect
Discover assets and potential vulnerabilities across your network. Know what's happening in your IT environment.
Want to see Bluehorn in action?
What makes Bluehorn different from other XDR solutions?
More tools don't necessarily mean better security
Organisations often invest in multiple cybersecurity solutions, but these tools don't always work together. Disconnected systems create blind spots, fragmented information and make it harder to identify real threats.
Bridging the gap between technology and expertise
Bluehorn brings your existing security solutions together in one XDR platform. Built on proven technology and powered by elite threat operations, it transforms scattered security data into actionable intelligence.
With greater visibility, intelligent threat detection and expert-backed response, Bluehorn helps your organisation stay ahead of evolving cyber threats.
European sovereignty. Greater control.
In a world where digital sovereignty matters more than ever, knowing where your security data resides and who controls it is essential.
Bluehorn brings a European approach to XDR, combining advanced security capabilities with European operational expertise. Giving organisations greater confidence in how their cybersecurity is managed.
How does Bluehorn's SOC support threat detection and response?
More than technology. Real threat operations behind your XDR.
Behind Bluehorn stands Easi's own Security Operations Center (SOC), bringing together experienced security professionals and threat analysts. European operational expertise, combined with advanced XDR technology, helps you identify, investigate and respond to threats around the clock.
With 24/7 monitoring and threat response capabilities, you benefit from expert support to identify, investigate and respond to abnormal behaviour and potential cyber threats.
What are the benefits of using Bluehorn?
Built for evolving security needs
Bluehorn adapts to your organisation's needs and security environment. It brings advanced threat detection and response capabilities together in one platform.
Proactive threat detection and response
Identify risks before they become threats. Detect suspicious behaviour and respond effectively with actionable insights for both management and IT teams.
Flexible and future-ready
Your security needs evolve. Bluehorn grows with your organisation, integrating with your existing security ecosystem and adapting to your changing security posture.
"For many years, I've worked with advanced cybersecurity solutions that weren't accessible to every organisation.
We saw an opportunity to bring the best of these technologies together in one solution: Bluehorn."
Jérémy Derzelle - Bluehorn Product Manager
Want to see more? Contact our experts
Also interesting for you